iGaming & Gaming
B2C operators, B2B suppliers, platforms, aggregators and affiliates.


International legal & regulatory advisory
ROZSUD advises gaming, fintech, payments and crypto businesses on the legal and regulatory work behind launching, getting paid and growing: licensing, financial crime compliance, banking, structuring, information security, data protection and AI governance — one senior team from first market entry to operating in several jurisdictions.
Industries
Our advice starts from how your sector is actually supervised, banked and financed — its regulators, payment partners and commercial logic — so what we deliver fits how your market works.
B2C operators, B2B suppliers, platforms, aggregators and affiliates.
Payment and e-money institutions, PSPs and acquirers, payment facilitators and embedded finance.
CASPs and VASPs, exchanges, custodians, wallets, token projects and crypto payments.
Forex and CFD brokers, investment firms, trading and investment platforms.
Online marketplaces, digital platforms, multi-sided platforms and digital service operators.
IT and software development companies, SaaS providers, IT outsourcing and cloud services.
Practice areas
Licensing, financial crime compliance, information security, data protection, AI governance, banking and structure are interdependent. We advise on them together, so each decision supports the others instead of reopening them.
All practice areasLicence strategy, applications and regulator engagement for gaming, payments, e-money, investment and crypto-asset businesses.
Group architecture, incorporation, substance and governance built around your licences, banking and investors.
Bank account opening, merchant accounts, acquiring, payment flows and safeguarding for international businesses, including gaming, crypto, forex and other high-risk models.
AML/CFT programmes, MLRO-as-a-Service, independent AML/CFT audits, risk assessments, monitoring, sanctions and inspection support.
External DPO services and working privacy programmes: GDPR and global privacy laws, DPIAs, data mapping, transfers and ISO/IEC 27701.
Fractional CISO support, ISMS and security programmes, certification and audit readiness, DORA, NIS2 and customer assurance for enterprise sales.
Governance that lets AI adoption scale: EU AI Act readiness, ISO/IEC 42001 management systems, AI risk and impact assessments, and vendor risk.
Trademark and patent registration, copyright, domain disputes and enforcement that protect your brand, software and content across markets.
Jurisdictions
The register covers 39 jurisdictions by region: who regulates what, and the licensing routes relevant to your sector. It is the starting point for weighing market access, banking acceptance, substance, timeline and reputation against your plans.
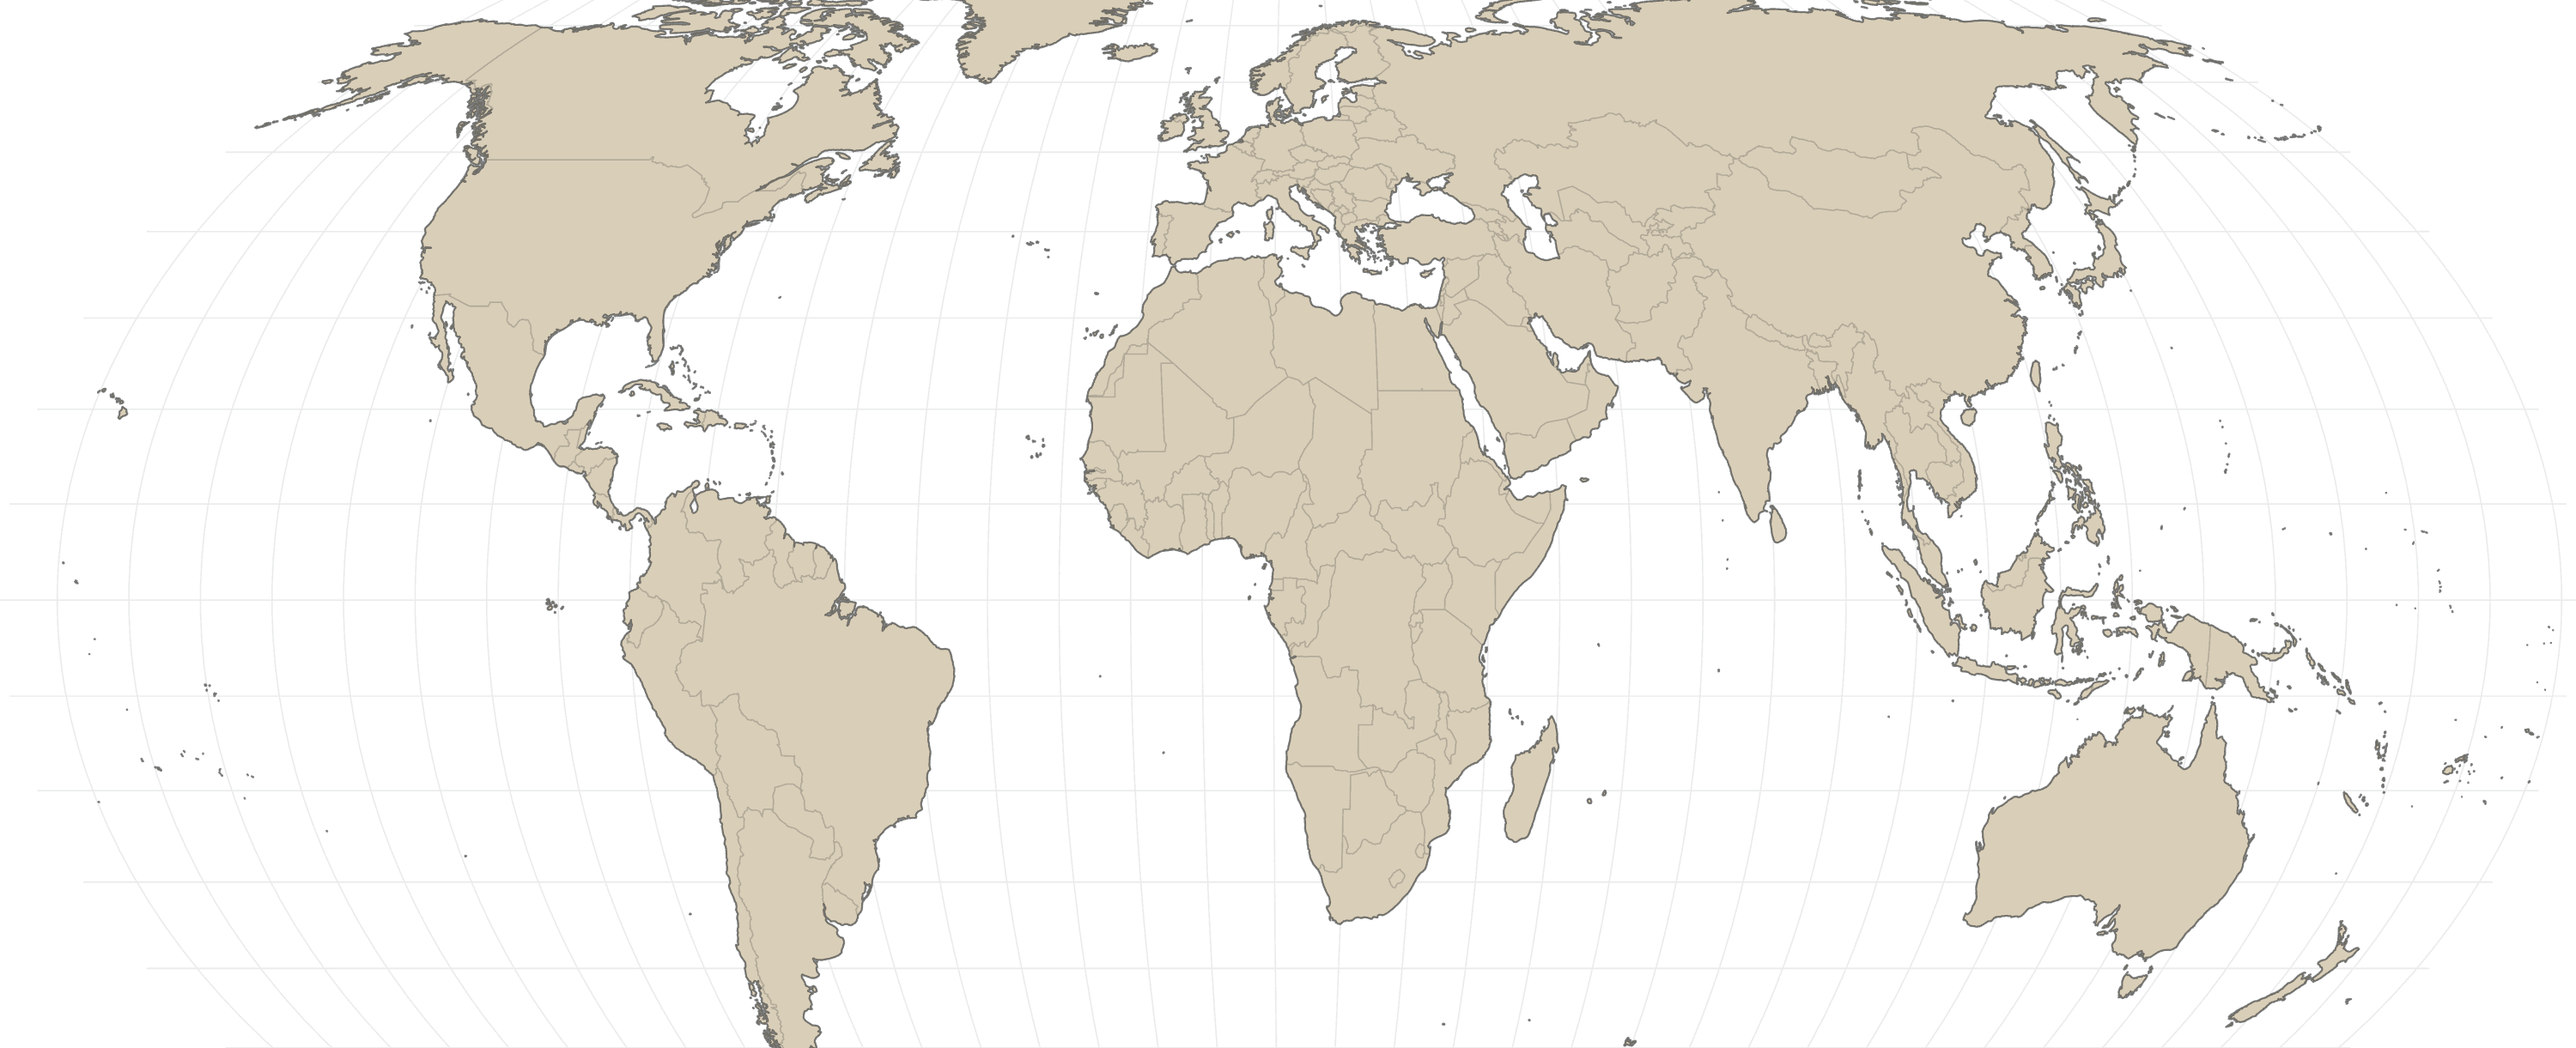
39 jurisdictions shown
Not sure which jurisdiction fits your model?
We compare candidate jurisdictions against your product, target markets, banking needs and budget — and recommend a route.
How we work
Regulated businesses rarely operate in one country. A gaming group may hold three licences, bank in a fourth jurisdiction and contract with suppliers in a fifth. We act as the single point of accountability across all of them.
The method
We map your business model, flows of funds and target markets against the regulatory perimeter in each jurisdiction, and agree what actually needs to be solved.
We design the structure: which entity does what, where, under which licence or exemption — and how banking, tax and governance fit around it.
We prepare applications, documentation and onboarding files, and coordinate local counsel and service providers against a single plan and timetable.
After launch, we help you keep the structure compliant as rules, products and markets change — with one team that already knows your business.
Parties we coordinate
Working with ROZSUD
Credibility in regulated industries is earned in the detail of each engagement. These are the commitments that define how we work.
Who we advise
The person who scopes your matter is the person responsible for delivering it. Work is not handed down to a junior team after the introduction.
You receive a written scope, timetable and fee proposal before any work begins, and we tell you in advance if the scope needs to change.
Documents are written for the people who review them — supervisors, bank compliance teams and auditors — to answer the questions they ask, not as generic templates.
We give you an early, candid view of whether a route is likely to work, whether a timeline is realistic and whether a structure will hold up, before you commit budget to it.
Advice is framed around business decisions: what it costs, how long it takes, what it unlocks and what the alternatives are.
Information about your business, plans and counterparties is handled on a need-to-know basis across every adviser we coordinate.
Insights & regulatory updates
Short, practical analysis of regulatory developments across gaming, payments, crypto and investment services.
Regulatory update · 6 min read
With MiCA's transitional periods over, the question for CASPs serving EU clients is whether their operating model matches the services they were authorised to provide.
Read the analysis
Practice note
6 min read
Consultation
Whether you are testing an idea, preparing an application or dealing with an urgent regulatory or banking issue, the first step is a discussion with a senior advisor.
Tell us about the matter
A few lines on your business, what you are planning and your timeline.
Initial conversation
A confidential call with a senior advisor on your goals, constraints and how we would approach the matter.
Written proposal
A clear scope, approach, timetable and fee before any work begins.
Enquiries are handled confidentially. A client relationship begins only once an engagement letter has been agreed in writing.